
ASOS Hack Sends Ransom Note
to App Users, Shares Fall 13%
A push notification titled “ASOS HACKED” landed on customers’ phones through the retailer’s own app, and the stock reacted within hours.
The ASOS hack reached customers in the most uncomfortable way possible: a push notification from the retailer’s own app. At around 10am BST on October 6, ASOS app users saw an alert titled “ASOS HACKED.” The text was addressed to the company’s data protection officer and IT team and claimed the attackers had “fully compromised the Snowflake instance,” ending with a demand to engage or see the data leaked. A Telegram link followed.
ASOS has confirmed “unauthorised activity involving third-party platforms” used to communicate with customers, and said personal details such as names and contact information may have been accessed. It says it does not believe payment card information or account passwords were affected. What it has not confirmed is the headline claim: that its Snowflake data platform was fully breached. No sample data has been published as of this writing.
This piece sorts out what’s confirmed and what isn’t, who the Xuanye Group appears to be, why the stock fell so fast, and what ASOS customers should do while the investigation continues.
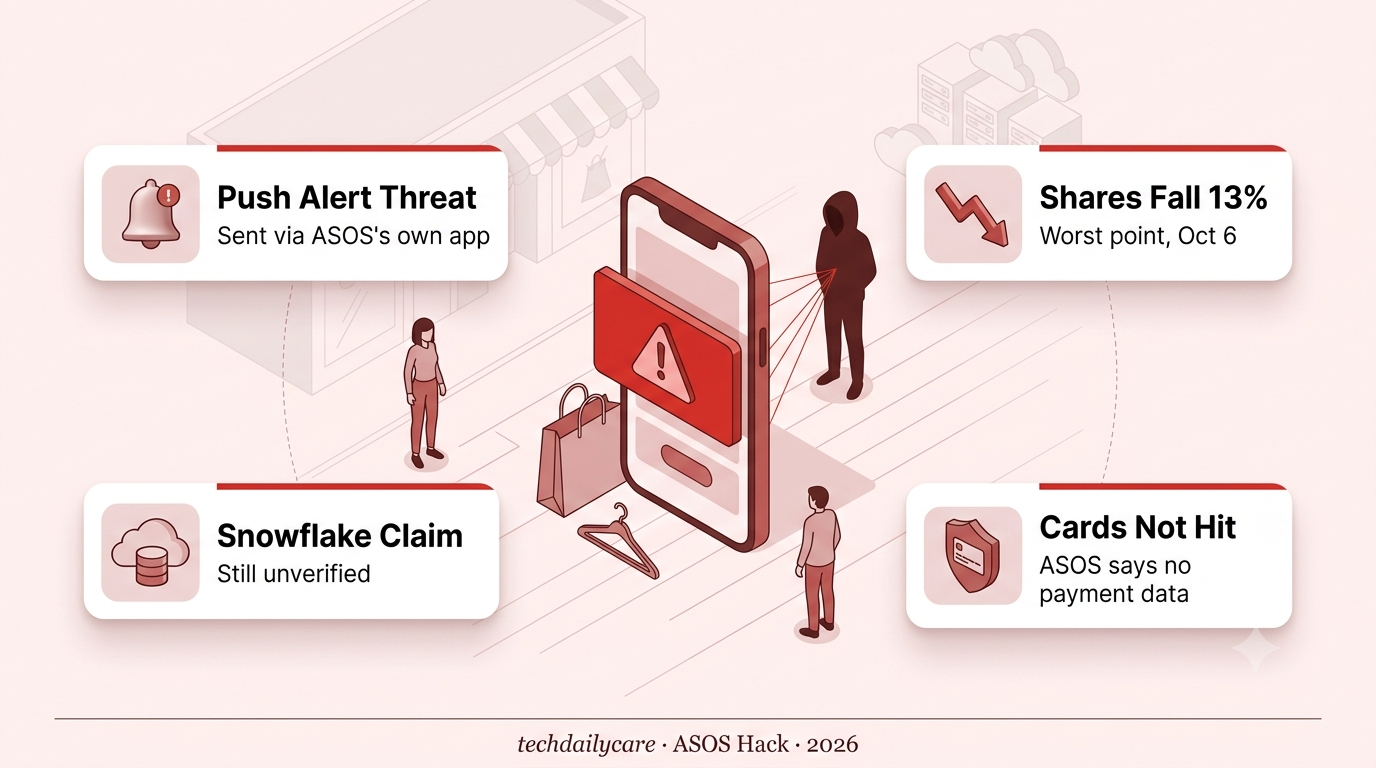
What Customers Saw
A push alert titled “ASOS HACKED,” sent through the official app, threatening a data leak unless the company engaged.
Who Claims It
A group calling itself Xuanye, whose Telegram channel appeared the same day. Researchers say it had no prior footprint.
What ASOS Confirmed
Unauthorised activity on third-party communication platforms, and possible access to names and contact details.
What’s Still Unverified
The claim that ASOS’s Snowflake instance was fully compromised. No stolen data has been shown publicly.
The ASOS Hack Starts With a Push Alert
The MessageThe alert read, in part, “Dear Asos DPO and IT, we have fully compromised the Snowflake instance. Engage with us, or we will leak it.” It was sent through the real ASOS app, which is what made it so alarming. Customers across the UK reported it, and screenshots spread quickly on Reddit and X, with some users saying they deleted saved payment details right away.
Who Is the Xuanye Group?
The ClaimantThe Telegram channel was created on the morning of the incident. Sophos told the Guardian that no one had mentioned the group on hacker forums or other Telegram channels before, and researchers who track extortion gangs said the name was new to them. In posts on the channel, the group claimed customer data was taken but said payment information was not affected and that the ASOS app was safe to use.
Why the ASOS Hack Points to Wider Access
The Technical ClueDan Bird of Horizon3 told the BBC that sending a push notification would require access to ASOS’s notification system, which is separate from the Snowflake data platform the attackers say they breached. ASOS’s own wording points the same way: the company says the unauthorised activity involved third-party platforms it uses to communicate with customers. In other words, the attackers clearly reached the messaging layer, even if the bigger Snowflake claim is unproven.
The Market Reaction: 13% in Hours
The FalloutASOS shares fell as much as 13.2% intraday, sliding from an opening price around 485p to a low near 435.5p, before paring some losses to trade roughly 9% to 10% lower. Snowflake’s own stock slipped by a small margin on the same news. ASOS has about 16.5 million customers, which is why investors treated even an unverified claim as a serious risk.
The hackers didn’t need to leak anything yet.
The notification did the damage.
- Don’t tap the Telegram link in the notification or reply to anyone claiming to be the hackers.
- Watch for phishing that mentions ASOS, since names and contact details may have been exposed.
- Change your ASOS password as a precaution and turn on two-factor authentication if it’s offered, even though ASOS says passwords weren’t affected.
- Use unique passwords so a leak at one retailer doesn’t unlock other accounts.
- Follow ASOS’s official channels for updates instead of screenshots circulating on social media.
⚠️ Why the ASOS Hack Still Matters If No Data Leaks
1. Reputation damage is instant. The share price dropped double digits before any evidence existed, which shows how powerful the threat itself has become.
2. Third-party platforms are the weak point. The incident involved services ASOS uses to talk to customers, a reminder that vendors can be an easier way in than the main systems.
3. Names and phone numbers are enough for scammers. Even without payment details, contact data fuels convincing phishing messages in the weeks after an incident.