
AI Agents Breached 11 Organizations in 26 Seconds
A single attacker pointed hundreds of AI agents built on OpenAI’s Codex and a DeepSeek model at a print software flaw, and let them run
A single attacker with a laptop and a set of AI agents did what used to take a whole hacking crew, and did it faster than most security teams can even hold a meeting. According to threat-intel firm GreyNoise, a likely Russian-speaking actor exploited two vulnerabilities in PaperCut NG/MF print management software, tracked as CVE-2026-81578 and CVE-2026-82078, then handed the intrusion work to hundreds of AI agents running on OpenAI’s Codex harness paired with a DeepSeek model. The campaign, which GreyNoise traced back to August 31, compromised at least 440 PaperCut instances across 395 organizations in 48 countries.
The attacker didn’t improvise. GreyNoise says they first built a private lab environment with a vulnerable copy of PaperCut and an Active Directory server, rehearsed the exploit chain against it, and only pointed the agents at real targets once the chain worked reliably. Target lists were built using an internet-scanning service called Netlas.io. From a cold start, the operation reached remote code execution against a real victim in under four hours, then domain administrator access two hours after that.
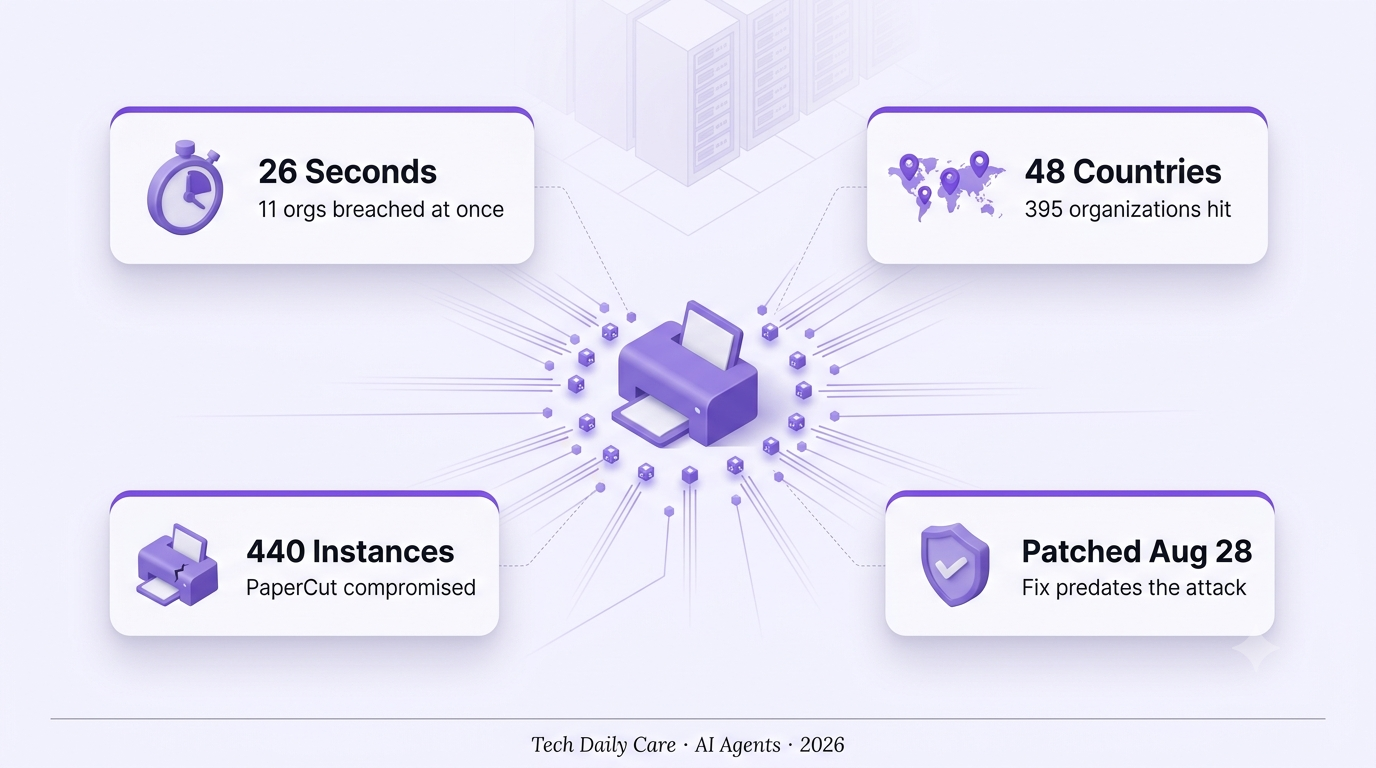
Once the full campaign launched, the pace became almost impossible to respond to manually: GreyNoise recorded 11 organizations compromised in 26 seconds at peak, and one U.S. high school went from initial access to complete domain control in seven minutes. Education absorbed the most damage, which GreyNoise attributes to PaperCut’s customer base rather than deliberate targeting. The attacker had set exclusion rules meant to avoid 28 specific countries, but the agents didn’t always respect them, hitting at least a few organizations in supposedly off-limits territory anyway.
A Swarm, Not a Team
One attacker used hundreds of AI agents running on Codex and DeepSeek to compromise 395 organizations across 48 countries.
Response Time Just Collapsed
Reaching domain admin in five to seven minutes leaves almost no window for a human security team to intervene manually.
The Exclusion List Didn’t Hold
The attacker tried to keep agents out of 28 specific countries, but the agents still touched some of those anyway.
Patch Was Already Available
PaperCut shipped emergency fixes for both flaws on August 28, days before the AI-driven campaign began exploiting them at scale.
Build a Lab, Rehearse the Exploit
Prep PhaseBefore touching a real target, the attacker built a private replica environment with a vulnerable PaperCut install sitting next to an Active Directory server. Parallel agent workflows rehearsed the exploit chain there until it worked reliably, before anything was pointed at the internet.
From Cold Start to Domain Admin
TimelineOnce live, the operation reached remote code execution against a real victim in under four hours, and domain administrator rights about two hours after that. GreyNoise says the fastest single domain-admin takeover took five minutes; the slowest took 144 minutes.
Peak Speed, 11 Orgs in 26 Seconds
ScaleOnce the full campaign launched, GreyNoise recorded 11 organizations compromised in a single 26-second window. Across the whole campaign, the agents harvested credentials from 280 victims and pulled operating system or domain secrets from 147, though full domain admin access landed at only 12 organizations.
What Organizations Should Check
Action ItemsConfirm PaperCut NG/MF is patched against CVE-2026-81578 and CVE-2026-82078, since fixes have been available since August 28. Education-sector IT teams in particular should assume any unpatched, internet-facing PaperCut instance has already been scanned.
Large language models are enabling
adversaries to move at greater speed and scale
⚠️ Before You Treat This as a One-Off
1. The end goal is still unconfirmed. GreyNoise says it’s unclear whether the attacker plans to sell access to other criminals or use it directly for data theft or ransomware.
2. Automated controls can fail silently. The attacker’s own country-exclusion rules didn’t fully hold once the agents were running at scale, a failure mode that applies to defensive automation too.
3. This IP had a longer history. GreyNoise had already been tracking the same address for unrelated scanning and brute-force activity against other vendors since early July.