
ShinyHunters Hacks in 2026, Rockstar, Kodak and More
Who the extortion gang hit, how they got in, and which numbers are confirmed versus only claimed.
Most people never hear from ShinyHunters directly. The first sign is usually an email from a company you forgot you gave your address to, saying “unauthorized third party” and “limited data.”
That is the odd part of this gang. They rarely go after you. They go after the vendor that holds your data on behalf of a hundred other brands, then post a countdown on a leak site and wait for the headlines to do the pressure work.
This article is a scorecard of 2026 so far. For each case you get what the victim confirmed, what the gang only claimed, and the one habit that would have made you safer.
Four Patterns Behind Every ShinyHunters Hack
The brands change. The playbook mostly does not.
The side door beats the front door
Stolen tokens from a SaaS integration, a misconfigured portal, or a convincing phone call. Not a movie-style break-in.
A public countdown does the work
Leak-site posts come with a deadline, usually days away. The goal is a rushed decision and maximum press coverage.
Claimed and confirmed rarely match
Victims say “limited.” The gang says millions. Both can be partly true until forensics finish.
Your data sits downstream
You are exposed through whoever stores your details, and the follow-up phishing is the part you actually feel.
They don’t pick the strongest lock.
They pick the weakest vendor.
How Big Are the Claims?
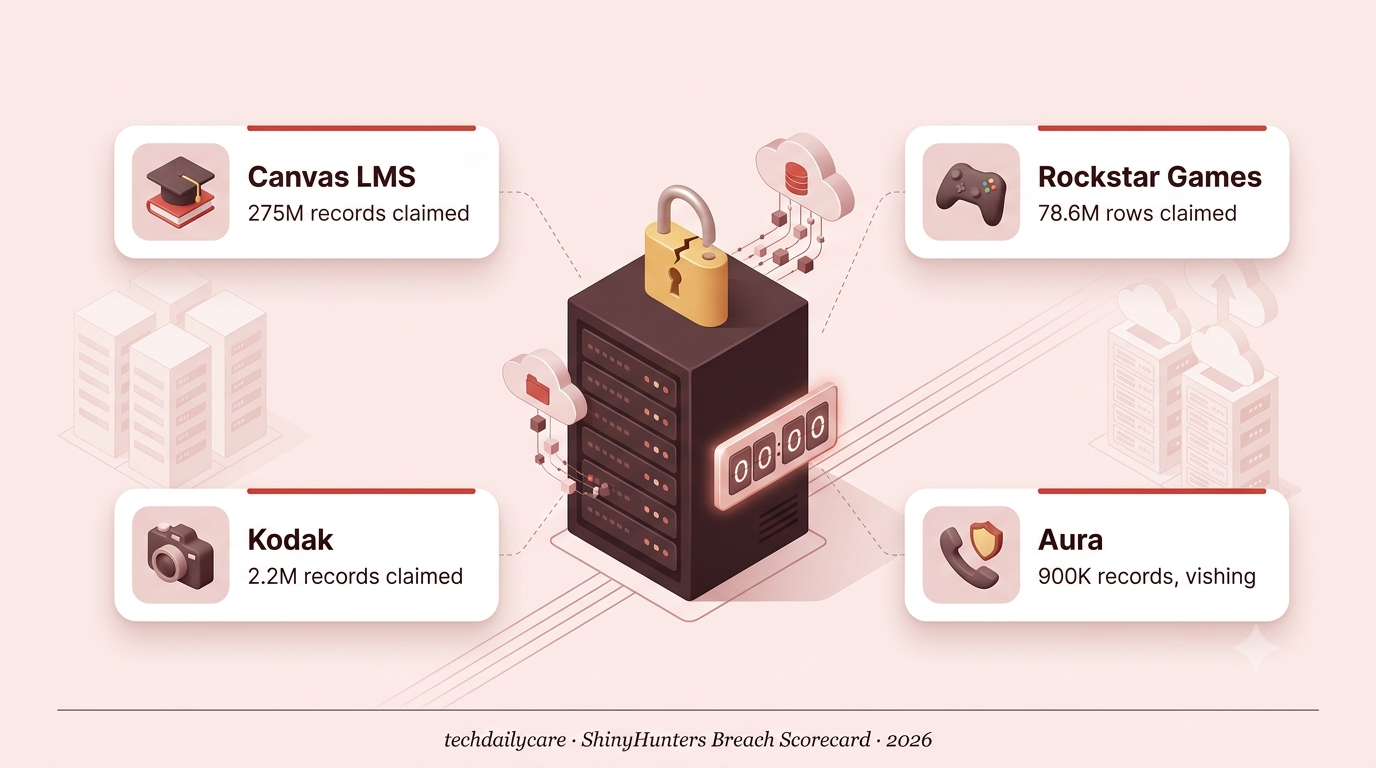
Record counts as claimed by ShinyHunters, not independently verified.
The 2026 Scorecard, Case by Case
What happened, what was confirmed, and what to take from it.
Canvas LMS (Instructure)
Confirmed + ClaimedIn late April, ShinyHunters hit Canvas, the learning platform used by thousands of schools. Instructure tied the second attack to its Free-For-Teacher accounts and took Canvas offline during finals week.
The gang claimed about 275 million records across roughly 9,000 schools and about 3.65 TB of data. On May 12, Instructure said it reached an agreement with the attacker and that the data was returned and destroyed. Several outlets reported a payment, but Instructure has not detailed the terms.
It was also Instructure’s second ShinyHunters incident in about eight months, after a September 2025 Salesforce breach.
Rockstar Games, twice in one year
Confirmed + ClaimedOn April 11, ShinyHunters posted a “pay or leak” message with an April 14 deadline. Reports say the way in was Anodot, a cloud-cost analytics vendor whose stolen authentication tokens unlocked connected Snowflake accounts.
Rockstar confirmed that a limited amount of non-material company information was accessed through a third-party breach, with no impact on players. The gang claimed 78.6 million records of internal analytics.
In September, ShinyHunters claimed a second Rockstar leak of about 8.1 GB, including anti-cheat components. That claim was unconfirmed when it was reported.
Kodak
Confirmed + ClaimedIn June, ShinyHunters claimed 2.2 million records of customer personal data and internal files, with a June 18 leak deadline. Kodak confirmed that an unauthorized third party temporarily accessed a limited set of company data.
Kodak has not said how the attackers got in or whether the claimed volume is accurate. That gap between “limited” and “2.2 million” was unresolved at the time of reporting.
Aura, via a phone call
ConfirmedIn March, ShinyHunters got into an Aura marketing database through vishing, which is voice phishing. About 900,000 records were taken. Even a security company was reached by a convincing call to the right employee.
Oracle PeopleSoft campaign and the long list
ClaimedIn June, the gang said it had compromised more than 100 organizations through hundreds of Oracle PeopleSoft instances. Reports in the same period tied the 2026 campaign to names such as Charter Communications, 7-Eleven, Medtronic, Vimeo, ADT and Vercel.
Claimed is not confirmed
ShinyHunters wants maximum fear, so its numbers lean high and its evidence often arrives late. Companies lean the other way and say “limited.” Until a regulator filing or a forensic report lands, the honest label for most figures here is alleged.
What you can do this week
You can’t stop the breach.
You can make the leak useless.
The Bottom Line
Protect your accounts before the next leak lands
Is Your Data on the Dark Web? Free Tools to Check for Leaks Nissan Just Lost Employee SSNs to Oracle’s PeopleSoft Zero-Day Passkeys vs Passwords, Why You Should Switch Right NowFAQ
Who is ShinyHunters?
A data-theft and extortion group active since 2019. It steals data, posts the victim on a leak site with a deadline, and demands payment to stop the release.
Was my data in the Rockstar or Kodak breach?
Rockstar said no player data was affected. Kodak said a limited set of company data was accessed. If your details were included, you should receive an official notice from the company.
Did Instructure pay ShinyHunters?
Instructure said it reached an agreement and that the data was returned and destroyed. Several outlets reported a payment, but the company has not disclosed the terms.
What is the single best thing I can do?
Stop reusing passwords and turn on passkeys or app-based two-factor on your key accounts. Leaked data is far less useful when each login is unique.
Editor’s note
Figures and dates come from public reporting by Help Net Security, BleepingComputer, Bitdefender, The Register, AP, Dark Reading, Malwarebytes and Mitiga as of October 12, 2026. Numbers attributed to ShinyHunters are the group’s own claims unless stated otherwise.